Substation protection and control: how an SPCS works and when to modernize
A protection and control system must recognize abnormal conditions, make selective decisions, command the interruption of the fault, and deliver reliable information about what happened to the operator. In an existing substation, modernizing this chain requires more than replacing relays: it requires understanding functions, circuits, interfaces, communication, risks, and operational constraints.
- Content:
- POWER Engineering
- Updated on
- September 2026
- Technical reading:
- approximately 25 minutes
Protection · Control · Automation · Supervision · IEC 61850 · Retrofit
In summary
Protection is a chain
The relay is one part of the system. Measurement, DC power supply, logic, trip circuits, breakers, communication, synchronization, and documentation all need to work together coherently.
Retrofit is an engineering decision
The age of the equipment is only one factor. Support, spare parts, performance, expansion capacity, security, records, and operational risk also determine the need for modernization.
Migration is part of the design
Between the existing system and the future architecture there is a critical stage: planning outages, temporary interfaces, tests, contingencies, and the entry into operation without losing essential functions.
What is a substation's protection and control system?
A substation must transfer energy, transform voltage levels, connect or isolate circuits, and keep the system within safe operating conditions. The equipment that physically performs these functions — power transformers, circuit breakers, disconnect switches, busbars, lines, cables, reactors, and capacitor banks — makes up the primary system.
The protection and control system is part of the secondary system. It monitors the electrical and operational behavior of the facility, processes information, identifies abnormal situations, executes commands, coordinates interlocks, records events, and makes data available to the operator.
In the context of this guide, SPCS means Protection, Control, and Supervision System. Depending on the standard adopted by the facility's owner, the acronym and the exact scope may vary. The concept, however, remains the same: bringing together the functions that make it possible to protect, command, automate, supervise, and analyze the substation's operation.
Four different functions, one single system
| Layer | Question it answers | Main function | Examples |
|---|---|---|---|
| Protection | Is there an abnormal condition that needs to be isolated? | Detect faults and inadmissible conditions and initiate the appropriate action | Overcurrent, distance, differential, breaker failure |
| Control | Can the switching operation be carried out, and by whom? | Process commands, permissives, blocks, and interlocks | Open, close, select local/remote, block a switching operation |
| Automation | What sequence must occur without depending on each manual command? | Coordinate logic, sequences, and automatic responses | Transfers, restoration, load shedding, and local automations |
| Supervision | What is happening and what happened? | Present states, measurements, alarms, events, and history | SCADA, HMI, SOE, trends, and remote control |
These layers have different objectives, but they share signals, devices, networks, documents, and test criteria. A seemingly localized change can affect permissives, alarms, remote commands, event records, and other functions that are not visible on the replaced panel.
How does a protection operation work?
A protection operation begins before the relay and ends after the breaker opens. Between the occurrence of the fault and the information presented to the operator there is a physical and logical chain that must remain intact.
The electrical system changes condition
A short circuit, ground fault, overload, loss of synchronism, or other abnormal condition changes the system's currents, voltages, frequency, impedance, or states.
The quantities are measured
Current and voltage transformers — CTs and VTs — provide signals compatible with the protection devices. In process-bus architectures, acquisition units can digitize these quantities and transmit them over the network.
The IED processes the information
The relay or intelligent electronic device applies algorithms, settings, timers, directional criteria, restraints, and logic defined by the protection philosophy.
Protection decides whether to operate
The decision must distinguish an internal fault from an external condition, a transient disturbance, or an admissible operating situation. Depending on the function, this decision can occur in milliseconds or include an intentional time delay for coordination.
The trip command travels through the chain
The IED output acts on the trip matrix, auxiliary relays, or communication messages defined in the design. The DC circuit energizes the opening coil of the corresponding breaker.
The breaker interrupts the current
The primary equipment opens its contacts and isolates the faulty part. If it does not interrupt the current within the expected time, the breaker-failure function can command the opening of backup breakers.
The system records and communicates
Events, alarms, oscillography, measurements, and states are recorded and sent to the supervisory system or the control center. This data makes it possible to reconstruct the event, verify protection performance, and guide corrective actions.
Reliability depends on the most vulnerable link
Select a link to see the consequence of its unavailability.
Measurement
What needs to be ensured — Ratio, polarity, class, circuit integrity, and adequacy of the CTs/VTs
Consequence of unavailability — The IED receives incorrect or insufficient quantities
DC power supply
What needs to be ensured — Voltage, autonomy, protection, and circuit continuity
Consequence of unavailability — The opening command may not reach the trip coil
IED
What needs to be ensured — Hardware, firmware, settings, logic, and configuration
Consequence of unavailability — The function may fail to recognize the condition or operate incorrectly
Trip logic
What needs to be ensured — Matrix, contacts, messages, and auxiliary relays
Consequence of unavailability — The correct decision does not reach the correct breaker
Breaker
What needs to be ensured — Interrupting capacity, mechanism, and coils
Consequence of unavailability — The fault remains energized despite the command
Recording and supervision
What needs to be ensured — Time, events, oscillography, and communication
Consequence of unavailability — The operator loses visibility and diagnostic capability
That is why replacing only the relay without validating the rest of the chain can renew a component while leaving the systemic risk in place.
What are the layers of an SPCS?

The architecture varies with the size of the facility, the voltage level, the criticality of the assets, the client's philosophy, and the technology applied. A useful way to understand it is to divide the system into functional levels.
Process level
This is where the secondary system meets the primary equipment. It includes current and voltage quantities, positions, contacts, commands, opening and closing coils, and interfaces with circuit breakers, disconnect switches, transformers, and other assets. In digital projects, it may include merging units and sampled-value communication.
Bay level
Concentrates functions associated with an electrical position: protection, control, measurement, interlocking, synchronization, reclosing, recording, and communication. Protection relays and bay controllers are typical devices at this level.
Station level
Integrates the bays and gathers common functions such as servers, HMI, gateways, concentrators, local supervision, recording, engineering, synchronization, and interfaces with higher-level systems.
Operation level
Connects the substation to the control center and to other corporate or operational systems. It includes remote control commands, alarm and event consolidation, remote visualization, and the data used for analysis and maintenance.
Physical architecture and functional architecture are not the same thing
Two systems can use similar equipment and behave very differently. The placement of functions, network segregation, redundancies, trip paths, control hierarchy, and interfaces with existing systems define the real architecture.
In a retrofit, it is essential to map both views:
- Physical: panels, devices, terminals, cables, fibers, switches, power supplies, and circuits.
- Functional: protections, logic, commands, interlocks, data, dependencies, and expected responses.
What makes protection technically reliable?
Effective protection is not simply fast. It must combine criteria that, in certain situations, compete with each other.
Selectivity
Isolate the smallest necessary part of the system, keeping unaffected areas in service. Selectivity depends on the philosophy, zone boundaries, studies, and coordination between main and backup protections.
Sensitivity
Recognize fault conditions within the protected zone, even when the available quantities are reduced or influenced by the system configuration.
Speed
Clear the fault in a time compatible with system stability, equipment withstand capability, and safety. The fastest operation is not always the most selective; the design determines where speed is essential and where coordination requires a time delay.
Dependability
Operate when the intended condition actually occurs. This depends on the combination of measurement, logic, power supply, trip circuits, and interrupting equipment.
Security against incorrect operation
Remain stable in the presence of external faults, transients, CT saturation, transformer energization, power swings, and other conditions that should not result in a trip.
Redundancy and independence
Critical facilities may require independent main protections, power sources, CT cores, trip circuits, communication channels, or redundant networks. Redundancy does not mean duplicating components without criteria: it is necessary to reduce common failure causes and verify the behavior when each element is lost.
Protection functions: the code identifies the function, it does not define the design
Function numbers are an established language for identifying devices and functions in electrical power systems. They help organize documents, diagrams, and logic, but they do not replace the application study.
| Code | Function | What it monitors | Common applications |
|---|---|---|---|
| 21 | Distance | Apparent impedance and fault direction | Transmission lines and circuits where current-based protection does not provide sufficient selectivity |
| 24 | Overexcitation | Voltage/frequency ratio | Transformers and generators subject to excessive magnetic flux |
| 25 | Synchronism check | Voltage, frequency, and angle difference | Closing breakers between sources or energized parts of the system |
| 27 / 59 | Undervoltage / overvoltage | Voltage below or above the limits | Busbars, machines, loads, and control or protection schemes |
| 32 | Directional power | Magnitude and direction of active power | Generators, motors, and interchange or flow control |
| 40 | Loss of excitation | Underexcitation or loss-of-field condition | Synchronous generators |
| 46 | Negative sequence or current unbalance | Negative-sequence component | Motors, generators, and phase-unbalance situations |
| 48 / 51LR | Excessive starting time / locked rotor | Current and time during starting or stall | Motors |
| 49 | Thermal protection | Thermal-condition model or measurement | Transformers, motors, generators, and cables |
| 50 / 51 | Instantaneous / time-delayed overcurrent | Phase current | Feeders, transformers, and backup protection |
| 50N / 51N | Neutral or residual overcurrent | Residual or neutral current | Ground faults, depending on grounding and the measurement method |
| 50BF | Breaker failure | Persistence of current and/or states after the trip | Local backup for opening adjacent breakers |
| 63 | Pressure, gas, or flow | Condition of mechanical devices associated with the equipment | Transformers and other equipment with their own detection devices |
| 67 / 67N | Directional overcurrent | Current and polarizing reference | Ring, meshed systems, or systems with bidirectional fault current flow |
| 79 | Automatic reclosing | Opening and restoration sequence | Lines and feeders, according to operating policy |
| 81 | Frequency | Underfrequency, overfrequency, or rate of change | Generation, islanding, stability, and system-wide schemes |
| 85 | Teleprotection channel | Permissive, blocking, or transfer signals between terminals | Communication-assisted line protection schemes |
| 86 | Lockout | Lockout command maintained after a given operation | Faults that require inspection before restoration |
| 87 | Differential | Vector comparison of the currents bounding a zone | Transformers, busbars, generators, motors, and lines |
The application changes according to the protected asset
| Asset | Functions frequently considered | Engineering considerations influencing the choice |
|---|---|---|
| Line or feeder | 21, 50/51, 50N/51N, 67/67N, 79, 85 | Topology, sources, grounding, teleprotection, selectivity, and stability |
| Transformer | 87T, 50/51, 50N/51N, 49, 63, 24, 86 | Ratio, vector group, magnetizing current, grounding, and dedicated protections |
| Busbar | 87B, 50BF, 86 | Zones, disconnect-switch position, CT saturation, speed, and stability |
| Generator | 87G, 32, 40, 46, 49, 59, 81 | Grounding, power, excitation, stability, thermal limits, and plant integration |
| Motor | 49, 46, 48/51LR, 50/51, 50N/51N, 27 | Starting, locked-rotor time, load, process, and operating regime |
| Capacitor bank or reactor | 50/51, 50N/51N, 59, 87, imbalance | Configuration, energization, harmonics, internal units, and grounding method |
The relationships above are for guidance only. The selection, setting, and coordination of the functions depend on the electrical studies, the topology, the equipment data, the owner's requirements, and the rules applicable to the project.
Control, automation, and supervision: operation must be predictable
While protection responds to abnormal conditions, control organizes how the facility must be operated. It establishes who can issue commands, under what conditions, and with what confirmations.
Command hierarchy
A piece of equipment can be commanded from the yard, from the panel, from the local HMI, or from the control center. The philosophy must define priorities, local/remote modes, blocks, and the conditions for transferring control between levels.
Interlocks
Interlocks prevent switching operations that are incompatible with the state of the system. They can combine breaker and disconnect-switch positions, presence of voltage, grounding, operating permissives, and other conditions. In a retrofit, simply reproducing inputs and outputs is not enough: the intent of the logic must be reconstructed.
Permissives and blocks
A command may depend on synchronism, spring charge condition, pressure, absence of a block, circuit availability, or authorization from another system. These signals need to be documented, tested, and presented to the operator in a way that is easy to understand.
Automation schemes
Transfers, restoration, reclosing, voltage control, starting sequences, and special schemes require a clear definition of initial states, advance conditions, timers, failure handling, and return to a safe condition.
Supervision and recording
The supervisory system organizes states, measurements, alarms, events, and commands. A well-designed screen does not compensate for an inconsistent database; quality starts at the signal source, passes through naming and alarm priority, and ends with the presentation to the operator.
The sequence-of-events record — SOE — and oscillography make it possible to reconstruct occurrences. For the analysis to be reliable, clocks, time zones, time quality, and record resolution need to be consistent throughout the architecture.
See how automation integrates IEDs, networks, SCADA, and operation in the guide dedicated to substation automation architecture.
IEC 61850: interoperability requires engineering
IEC 61850 should not be treated as just a protocol. The series structures data models, communication services, and a system description language, making it possible to represent functions and exchange information between devices and engineering tools.
MMS
It is used in client-server communication to make states, measurements, alarms, commands, and other data available between IEDs and supervision or control systems.
GOOSE
It enables fast exchange of events and states between devices. It can be applied to interlocks, permissives, blocks, transfers, and protection-related signals, depending on the architecture. Its use requires publish/subscribe engineering, supervision, testing, and configuration management.
Sampled Values
Sampled Values make it possible to digitally transmit current and voltage quantities. They are associated with process-bus architectures and require specific network, timing, availability, testing, and maintenance requirements. Not every IEC 61850 installation uses Sampled Values.
SCL
The SCL language describes devices, capabilities, communication, and the system configuration. Files such as ICD, CID, and SCD are part of the engineering cycle and need to be controlled as technical documents, with version, origin, ownership, and correspondence with the system in operation.
Compatibility is not a guarantee of interoperability
Two pieces of equipment declared compatible with IEC 61850 do not automatically form an integrated system. Data models, standard editions, service implementation, naming, datasets, messages, tools, and client requirements need to be reconciled and tested.
Networks, availability, and timing
Topology, segregation, capacity, latency, synchronism, and redundancy must result from the functional requirements. Protocols such as PRP and HSR can provide seamless recovery from certain network failures when planned and correctly implemented. They do not eliminate the need to analyze power sources, switches, links, configurations, and common failure causes.
Integration with legacy systems
Modernizations often require different generations to coexist. Gateways, converters, physical contacts, and legacy protocols may remain during one stage or throughout the system's entire life cycle. The solution must preserve the meaning of the data, command security, time quality, and diagnostic capability.
Learn about POWER's approach to IEC 61850 integration.
Without DC power, there is no reliable trip chain
The DC system keeps relays, controllers, communication, signaling, and command circuits available even when the facility's AC supply is lost. It also provides the energy needed for the breakers' opening and closing coils, depending on the architecture.
Rectifiers, battery banks, distribution panels, protection devices, cables, and supervision form another critical system. Rated voltage, autonomy, selectivity, charger capacity, steady-state current, transient loads, and battery condition need to be considered together.
In a protection and control retrofit, the following must be verified:
- available capacity of the DC system;
- minimum voltage at the terminals of critical loads;
- voltage drops in the trip circuits;
- required autonomy;
- circuit distribution and protection;
- ground-fault supervision and alarms;
- impact of new loads;
- condition, age, and documentation of the battery bank;
- strategy for maintaining power supply during the migration.
POWER integrates this need into SPCS projects and, when the scope requires power-conversion solutions, works with technology from NPT Energia, a MACH Capital group company specialized in DC systems for critical applications.
When does a protection and control system need a retrofit?
There is no universal age at which every SPCS must be replaced. An older system can remain adequate if it is supported, documented, testable, and compatible with the facility's needs. Likewise, a relatively new system can present a risk if its architecture, configuration, or maintenance are inadequate.
The decision must combine life cycle, condition, performance, and operational exposure.
Life cycle and support
- Relays, controllers, servers, or switches that are end-of-line.
- Lack of reliable replacement parts.
- Engineering tools incompatible with current computers.
- Dependence on cables, ports, or operating systems that are difficult to maintain.
- Firmware without support or without the possibility of necessary fixes.
Performance and reliability
- Incorrect operations or failure to operate.
- Intermittent communication failures.
- Recurring restarts or faults.
- Event records insufficient to clarify occurrences.
- Unavailability that increases as the installed base ages.
Maintainability
- Configurations that cannot be located or lack version control.
- Diagrams and signal lists that differ from the actual installation.
- Knowledge concentrated in a few people.
- Equipment that cannot be tested with the available resources.
- Recovery time incompatible with the criticality of the asset.
Integration and expansion
- Lack of capacity for new bays, signals, or functions.
- Proprietary protocols that limit integration.
- Supervision lacking information necessary for operation.
- Difficulty standardizing IEDs or incorporating new systems.
- Architecture that does not meet the facility's future requirements.
Security and operational risk
- Discontinued operating systems.
- Shared accounts or access without traceability.
- Lack of validated backups and a recovery procedure.
- Networks without segregation consistent with the criticality of the facility.
- Frequent interventions in old, poorly documented circuits.
Decision guidance matrix
| Condition | Decision trend |
|---|---|
| Supported equipment, intact documentation, satisfactory performance, and expansion capacity | Maintain, test, and monitor |
| Isolated points of obsolescence, overall healthy architecture | Targeted replacement or directed upgrade |
| A family of IEDs or a system layer at end of life | Retrofit by system or by function |
| Bays with different criticality levels and limited outage windows | Progressive modernization by bay |
| Widespread obsolescence, fragile documentation, and systemic limitations | Planned re-engineering and full retrofit |
The table is for guidance only. The final decision depends on field surveys, documents, criticality, operating requirements, and applicable studies. The decision requires an assessment of the facility and the project's requirements.
Partial, by-bay, or full retrofit?
Retrofit does not necessarily mean replacing the entire system. The right scope is the one that reduces the relevant risk without creating an architecture that is difficult to maintain.
Targeted replacement
Recommended when a component is clearly obsolete or faulty and the rest of the architecture remains adequate. It requires checking electrical, functional, mechanical, logic, and communication compatibility.
Advantage: smaller immediate intervention.
Attention: may transfer the obsolescence to the interfaces and keep systemic limitations in place.
Retrofit by bay
Modernizes one electrical position at a time, keeping the others in operation. It is a common alternative when outage windows are short or when the investment needs to be spread out.
Advantage: progressive implementation.
Attention: requires managing interfaces between new and old bays throughout the entire transition.
Retrofit by layer or system
Replaces a cross-cutting function, such as supervision, communication, synchronization, or a specific family of IEDs.
Advantage: standardizes a common limitation.
Attention: may require adaptations across a large number of retained devices.
Full retrofit
Redesigns protection, control, automation, supervision, and communication when obsolescence and limitations are extensive or when the facility will undergo significant expansion.
Advantage: coherent architecture, ready for the next cycle.
Attention: demands more extensive migration engineering, testing, and outage planning.
Legacy, transition, and future architecture
An older system can remain adequate if it is supported, documented, testable, and compatible with the facility's needs.
During a progressive modernization, the temporary system is a real operating state. It can bring together equipment from different generations, physical and digital signals, new and old networks, and partially migrated supervision databases.
This state must have:
- dedicated diagrams
- interface list
- validated logic
- clear boundaries of responsibility
- test plan
- rollback or contingency procedure
- documentation of each completed stage
Redesigns protection, control, automation, supervision, and communication when obsolescence and limitations are extensive or when the facility will undergo significant expansion — a coherent architecture, ready for the next cycle.
How is an SPCS retrofit carried out?

A safe modernization starts with the system that is actually in operation, not just the set of available drawings.
Survey and reconstruction of the current state
Inspection of the installed base, panels, IEDs, circuits, terminals, networks, versions, signals, logic, files, documentation, environmental conditions, and access or outage constraints. The result should be a reliable as-is representation: the system as it actually exists and operates.
Criticality and obsolescence assessment
Classification of assets and functions according to failure consequence, condition, support, spare parts, maintenance, cyber exposure, recovery capability, and expansion needs.
Definition of the philosophy and future architecture
Definition of protection zones, functions, redundancies, control hierarchy, networks, synchronization, supervision, interfaces, power supply, performance requirements, and test criteria.
Detailed engineering
Development or review of functional and construction diagrams, signal lists, logic, trip matrices, interlocks, databases, parameter settings, configurations, screens, networks, and migration documentation.
Configuration, integration, and factory testing
Configuration of IEDs, controllers, switches, gateways, and the supervisory system. Individual and integrated validation of the functions before the field intervention, according to the scope and simulation capability.
Migration and commissioning
Phased execution, circuit identification, blocking, signal transfer, point-to-point testing, functional testing, command validation, energization, and monitoring of the entry into operation.
Final documentation and support
Consolidation of as-built records, native files, backups, test reports, version records, training, and the information needed for operation, maintenance, and future changes.
Critical points of the migration
Current circuits
CT secondaries require specific handling and safe procedures. Changes, tests, and isolation must consider the risk of inadvertently opening the circuit and the correspondence between polarities, ratios, cores, and functions.
Trip circuits
Each path must be traced from the IED to the breaker coil, including contacts, auxiliary relays, test switches, blocks, supervision, and power supply. Testing only the relay's logic output does not validate the full chain.
Interlocks and permissives
Existing logic may be distributed across wiring, auxiliary relays, IEDs, controllers, and the supervisory system. The migration must preserve the intended behavior, eliminating improper dependencies and documenting approved changes.
Temporary interfaces
Each signal between the new system and the retained system must have a defined origin, destination, safe state, quality, failure handling, and test criteria.
Rollback plan
Before starting a critical outage window, it is necessary to define how far the implementation can be reverted, which conditions allow progress, and which evidence authorizes release for operation.
See how POWER structures engineering, configuration, integration, and field services.
What can go wrong in a poorly planned retrofit?
The most significant risks are usually found in the interfaces and in the functions that were not explicitly reconstructed.
Equivalent swap only on paper
A new IED can have the same ANSI functions and still differ in inputs, outputs, logic, timing, filtering, supervision, communication, and behavior during transient conditions.
Incomplete documentation treated as ground truth
Outdated diagrams can omit changes made in the field. An implementation based solely on the document can remove an existing function or create an incorrect interface.
Focus on the relay and lack of a systemic view
Measurement, DC power supply, trip circuit, breaker, supervision, and remote control can remain unvalidated even when the new IED is correctly configured.
Interlock rebuilt without operational context
Converting contacts into digital logic without understanding the intent of the switching operation can produce unnecessary blocks or allow improper commands.
Communication validated only by connectivity
A device responding on the network does not prove the meaning, quality, timeliness, or behavior of the data during failures.
Fragmented testing
Equipment approved in isolation can fail when integrated. Validation needs to include the complete paths and the relevant operating and contingency scenarios.
Configuration without governance
Files without identification, version, an owner, and correspondence with what is installed make future maintenance slow and risky.
What tests are needed before entering operation?
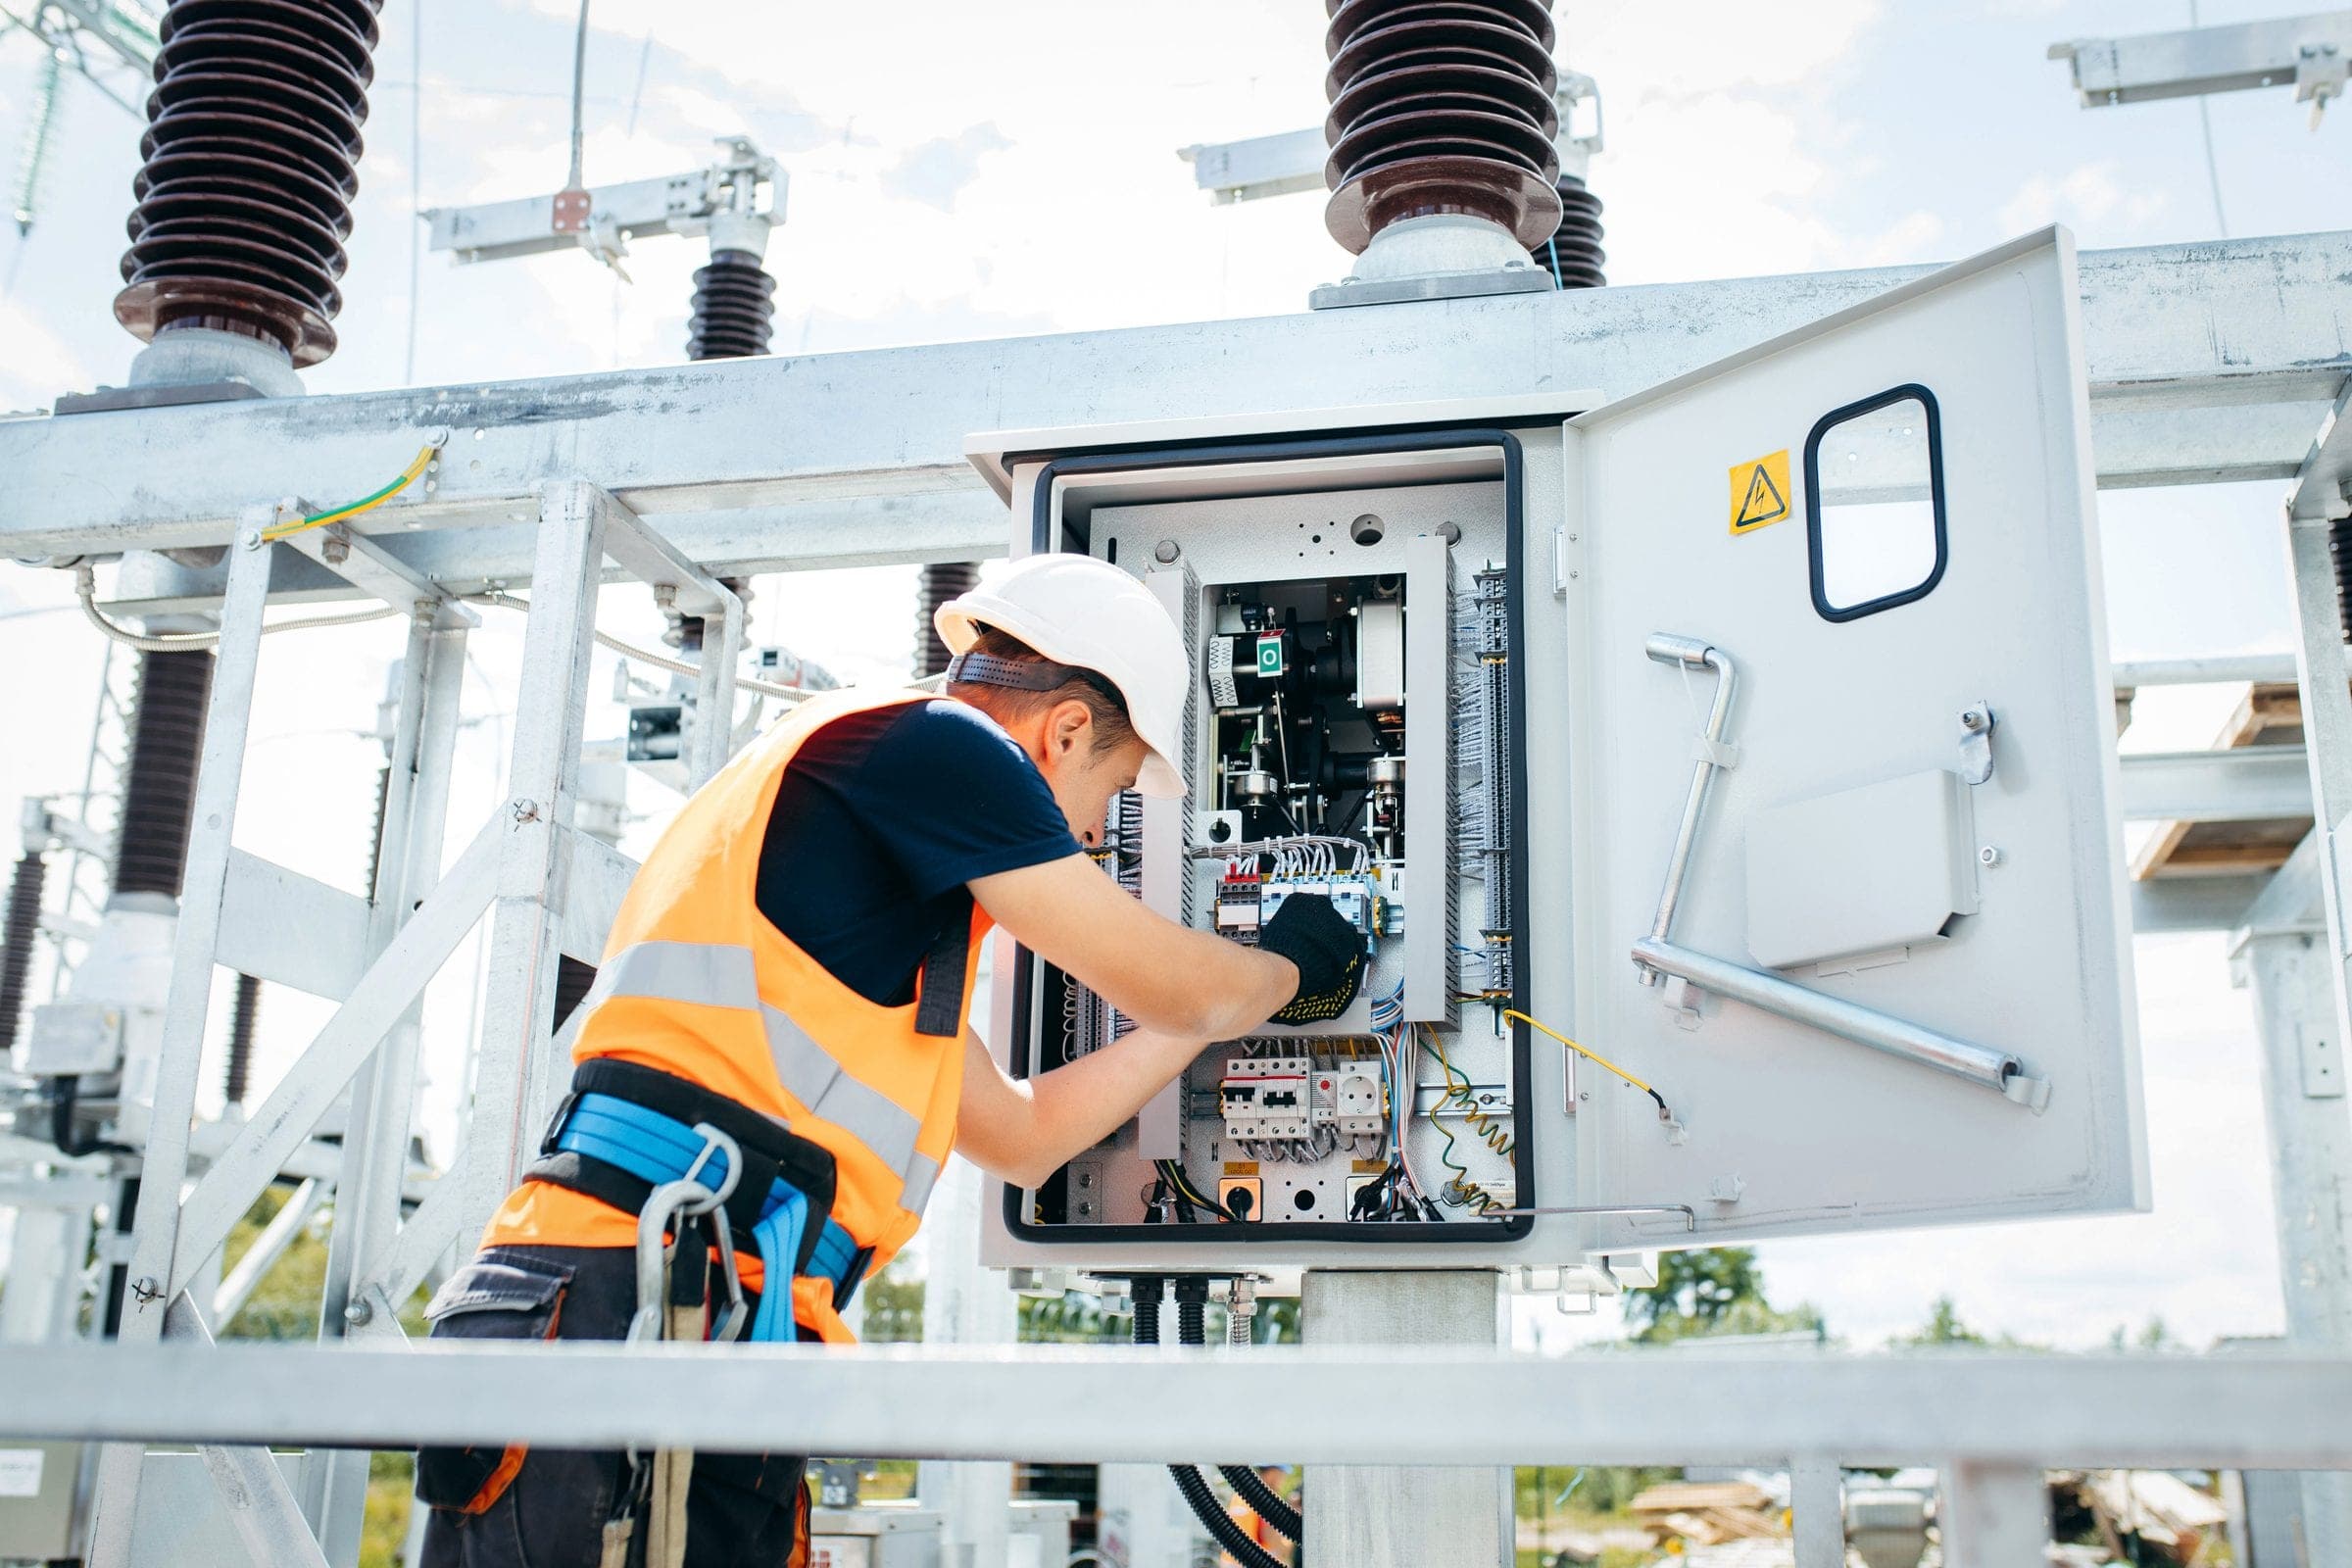
The test plan must be developed together with the architecture and the philosophy. It needs to demonstrate that requirements and functions have been met, not just that each piece of equipment powers up or communicates.
| Test group | What must be verified |
|---|---|
| Inspection and documentation | Identification, assembly, terminals, cables, fibers, versions, drawings, and correspondence with the design |
| DC power and circuits | Polarity, protection, supervision, voltage drops, commands, and continuity of critical circuits |
| Inputs and outputs | States, polarities, scales, contacts, commands, alarms, and position feedback |
| Protections | Pickup quantities, timers, direction, restraints, zones, blocks, and associated signals |
| Logic | Trip matrices, interlocks, permissives, automation schemes, failures, and feedback states |
| Communications | Datasets, reports, commands, GOOSE, protocols, quality, link loss, and recovery |
| Synchronization | Time source, quality, distribution, loss of reference, and record consistency |
| Supervision | Screens, naming, alarms, priorities, measurements, SOE, history, and remote control |
| Redundancy | Behavior when a power source, server, switch, link, or other planned element is lost |
| Point-to-point | Correspondence between each physical or logical source and its destination |
| Integrated functional | Complete system response for protection, control, failure, and contingency scenarios |
| End-to-end | Performance of the path between terminals or systems when the function depends on remote communication |
FAT, SAT, and field tests
The FAT makes it possible to anticipate problems before installation, especially in logic, communication, databases, and integration. The SAT confirms the solution in the real environment. Field tests validate circuits, polarities, interfaces with primary equipment, and conditions that cannot be fully reproduced in the factory.
The distribution between these stages depends on the scope, the architecture, and the client's requirements. What matters is maintaining traceability between requirement, function, procedure, result, and open item.
What must remain after commissioning
- test report and evidence;
- list of closed or formally addressed open items;
- as-built drawings;
- native files and backups;
- firmware and software version list;
- system configuration files;
- approved parameters and settings;
- communication matrix;
- logic documentation;
- recovery procedures;
- record of changes made in the field;
The actual deliverables must follow the limits and responsibilities defined in each contract.
How do you assess whether your SPCS is ready to keep operating?
Before deciding on maintenance, an upgrade, or a retrofit, gather evidence. This checklist does not replace an engineering assessment, but it helps identify gaps.
Assessment checklist
Protection and control system assessment checklist
POWER — Substation Protection, Control, and Automation · bepower.com.br
Frequently asked questions about substation protection, control, and retrofit
What does SPCS mean?
SPCS is an acronym used for Protection, Control, and Supervision System. It represents the set of devices, circuits, networks, logic, software, and documents that make it possible to protect, command, automate, and supervise an electrical facility. The exact name and scope can vary according to the owner's standard.
What is the difference between a protection relay and an IED?
A protection relay is the equipment dedicated to performing protection functions. IED, or intelligent electronic device, is a broader term for digital equipment capable of measuring, processing, communicating, and executing protection, control, or automation functions. Many of today's numerical relays are also IEDs.
What is the difference between protection and control?
Protection identifies abnormal conditions and initiates actions to limit their effects, normally by isolating the faulty part. Control processes commands, permissives, blocks, and interlocks so that equipment is operated under the intended conditions. The two functions are integrated, but they have different objectives and criteria.
What is SPCS retrofit?
It is the planned modernization of the protection, control, and supervision system of an existing facility. It can include relays, controllers, panels, circuits, communication, SCADA, synchronization, power supply, and documentation. The retrofit can be targeted, by bay, by layer, or full.
Is retrofit just replacing old relays with digital relays?
No. Replacing the relay may be part of the scope, but the retrofit must also consider measurement, trip circuits, logic, interlocks, supervision, communication, DC power supply, primary equipment, testing, and the migration strategy.
When should a protection relay be replaced?
There is no single age that applies to all equipment. The decision should consider manufacturer support, availability of spare parts and tools, condition, performance, failure records, expansion capability, compatibility with the architecture, and the consequence of an outage.
Is it possible to retrofit without replacing all the panels?
Yes. In many projects it is possible to preserve panels, wiring, or part of the installed base, provided their condition and suitability are verified. The decision should evaluate space, terminals, circuits, insulation, power supply, interfaces, documentation, and the expected service life of the assembly.
Is it possible to integrate new IEDs with legacy equipment?
Yes, as long as the interfaces are technically compatible and tested. Integration can use physical contacts, protocols, gateways, or hybrid solutions. It is necessary to preserve the meaning of the signals, timing requirements, command security, and diagnostic capability.
Does IEC 61850 eliminate all conventional wiring?
No. The standard allows architectures with different degrees of digitization. A substation can use IEC 61850 on the station bus while keeping conventional circuits at the process level. Wiring reduction depends on the architecture adopted, the use of GOOSE, Sampled Values, merging units, and the project's requirements.
Are IEC 61850 devices automatically interoperable?
Not automatically. The standard creates a common basis, but effective interoperability depends on data models, services, editions, tools, configuration, architecture, and testing. Each device's conformance statement does not replace testing of the integrated system.
Does a retrofit require shutting down the entire substation?
Not always. The outage depends on the architecture, shared circuits, the implementation strategy, and operating conditions. Modernizations by bay or by phase can limit the extent of the outages, but the temporary interfaces and outage windows still need to be planned.
What are the main documents of a retrofit?
The set varies by contract, but it typically includes a survey of the existing system, architecture, philosophy, diagrams, signal lists, logic, trip matrix, network and communication, parameter settings, test and migration procedures, reports, and as-built documentation.
How do you start a protection and control modernization?
Start with an assessment of the existing facility. Gather documents and files, carry out a field survey, identify obsolescence, classify critical functions, and define operating requirements. Technology selection should come after the architecture and migration strategy have been defined.
Before choosing new equipment, understand the system that will keep operating around it.
POWER assesses, designs, configures, integrates, and deploys protection, control, supervision, and automation systems, taking into account the installed base, critical functions, and the real conditions of migration.
Technical note
This content presents general engineering concepts and does not replace electrical studies, owner requirements, risk analysis, safety procedures, or project-specific documentation. Functions, settings, architectures, tests, and implementation strategies must be defined by qualified professionals and in accordance with applicable standards and requirements.
Technical basis and references
- 1.IEC 61850 Series — Communication networks and systems for power utility automation. International Electrotechnical Commission.
- 2.IEC 60255-1:2022 — Measuring relays and protection equipment — Common requirements. International Electrotechnical Commission.
- 3.IEEE C37.2-2022 — Electrical Power System Device Function Numbers, Acronyms, and Contact Designations. IEEE Standards Association.
- 4.IEC 62439-3:2021 — High-availability automation networks — PRP and HSR. International Electrotechnical Commission.
- 5.IEC 62351 Series — Data and communications security for power systems. International Electrotechnical Commission.
- 6.Applicable Grid Procedures — Operador Nacional do Sistema Elétrico and Agência Nacional de Energia Elétrica, Brazil, according to the project's regulatory classification.
- 7.Requirements, standards, and specifications of the facility owner, applicable to each project.
We do not reproduce extensive excerpts from the standards. The references indicate the technical basis; application should consider the editions contractually required for each project.